What 75 days means
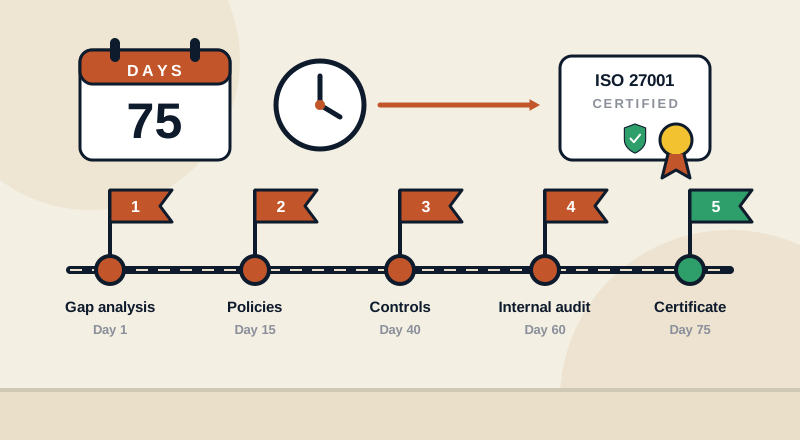
Our target is a complete Stage 2 audit within 75 days of kickoff, for a defined scope, with an engaged team, subject to certification-body scheduling. It is a target for well-scoped engagements, not a promise for every project, and we confirm an achievable date against your scope at kickoff.
The five stages
- Scope and kickoff: agree the boundary, timeline and responsibilities.
- Gap diagnostic: assess your current posture against every requirement and produce a prioritised remediation plan.
- Build: write the policies, procedures and controls and implement them with your team on a weekly cadence.
- Operate: run the management system so it generates evidence, including the internal audit and management review.
- Audit support: prepare the evidence package and sit alongside you through the audits.
Why the operating period sets the floor
The standard requires the ISMS to have operated before Stage 2, including an internal audit and a management review. You cannot skip that, so it sets the practical minimum. Compressing everything else around it, with early scoping and a certification body booked in advance, is how a short timeline becomes possible.
What makes 75 days realistic
- A tight scope limited to the product, people and infrastructure handling customer data.
- A responsive team that makes decisions and provides evidence quickly.
- The certification body booked early, because audit dates depend on their availability.
- Reasonable starting maturity, such as basic access control and logging already in place.
What slows it down
Large or fuzzy scope, slow approvals, controls that need engineering work to implement, and certification-body availability. A gap diagnostic tells you early which of these apply to you, so the date you commit to is honest.
Where Stage 1 and Stage 2 fit
Stage 1 is a documentation review where the auditor checks your ISMS is designed correctly. Stage 2 is the implementation audit, where they verify the controls are operating. We attend both with you.
Next step
A short scoping call is enough to tell you whether 75 days is realistic for your company. See our ISO 27001 page and our guide for UK startups, or book a free advisory session.