How to Choose an ISO 27001 Consultant: 7 Questions to Ask
Seven practical questions to ask before hiring an ISO 27001 consultant: who does the work, timeline, certification body, what is included and what is not.
Read more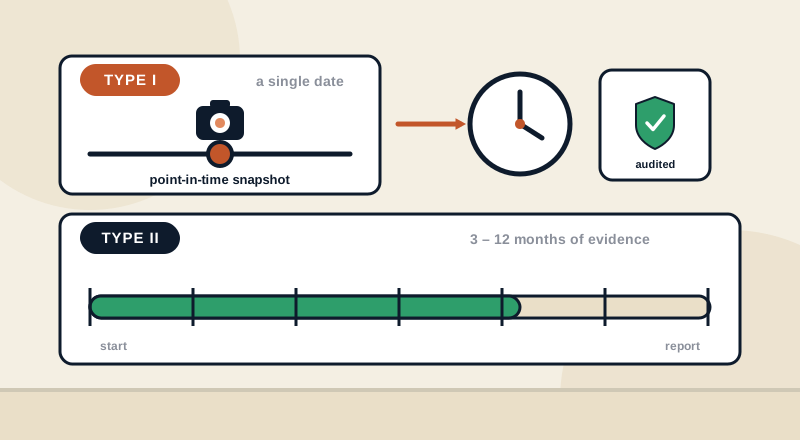
SOC 2 Type I vs Type II for US SaaS Companies
SOC 2 Type I or Type II? What each report proves, how long they take, and how SaaS startups usually sequence them to close US deals.
Read more
HIPAA for Health-Tech Startups: A Practical Starting Guide
HIPAA basics for health-tech startups: business associates, the Security Rule, risk analysis, BAAs and how HIPAA fits with SOC 2 and ISO 27001.
Read more
UK GDPR vs EU GDPR: What Changes for Your Business
UK GDPR and EU GDPR share the same core principles but differ in regulators, transfers and representatives. A practical guide for companies serving both.
Read more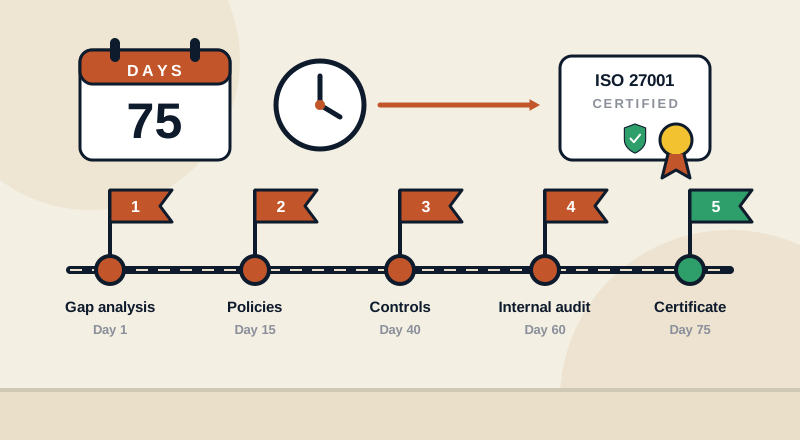
What a 75-Day ISO 27001 Timeline Actually Includes
How a Stage 2 ISO 27001 audit within 75 days works: the stages, the conditions that make it realistic and what can slow it down.
Read more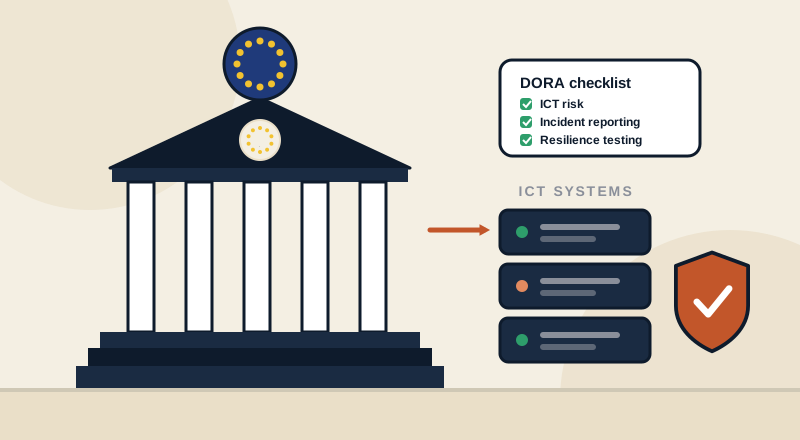
DORA Compliance Checklist for EU Fintechs
A practical DORA checklist for EU fintechs and their ICT suppliers: ICT risk management, incident reporting, resilience testing and third-party risk.
Read more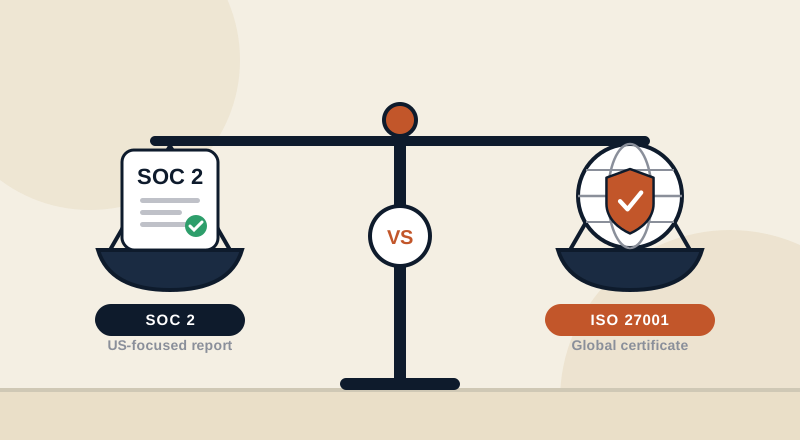
SOC 2 vs ISO 27001: Which Do You Need?
SOC 2 or ISO 27001? How they differ, who asks for each, how long they take and when it makes sense to pursue both. A practical guide for SaaS companies.
Read more
ISO 27001 for Startups in the UK: Where to Start
A practical guide for UK startups: when to pursue ISO 27001, how to scope it, what it takes, how long it runs and the mistakes that slow teams down.
Read more