The short answer
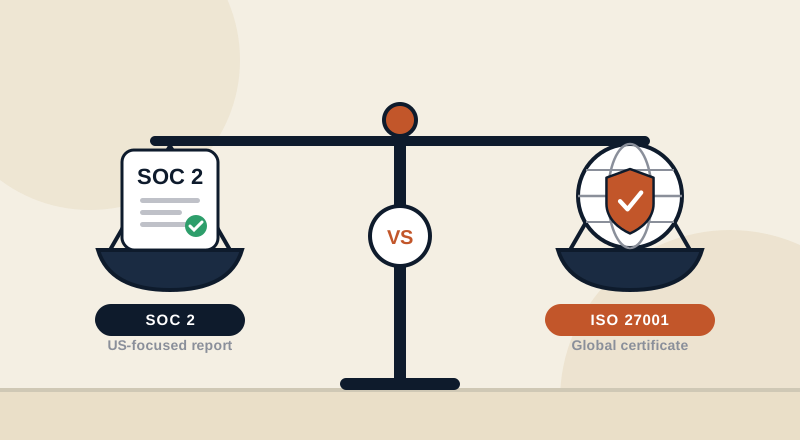
If most of your customers are in the US, start with SOC 2. If they are in the UK, Europe or international markets, start with ISO 27001. If you sell to both, plan them together, because the controls overlap significantly and evidence collected once can serve both.
What each one is
ISO 27001 is an international standard for an information security management system (ISMS). A certification body accredited for the standard audits you in two stages and issues a certificate, valid for three years with annual surveillance audits in between.
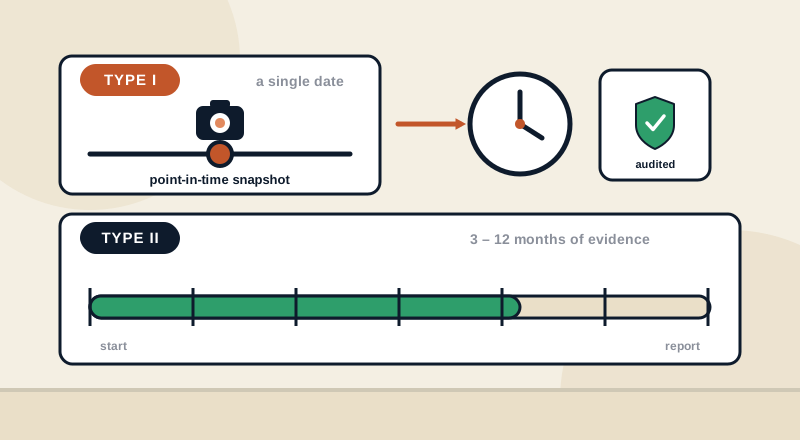
SOC 2 is an attestation report. An independent licensed CPA firm examines your controls against the AICPA Trust Services Criteria and issues a report. A Type I report describes whether controls are suitably designed at a point in time. A Type II report tests whether they operated effectively over an observation period, typically three to twelve months.
Who asks for which
US enterprise and mid-market buyers most often ask for a SOC 2 report, usually Type II. Buyers in the UK, Europe and many international markets, as well as financial institutions and public-sector bodies, more often ask for an ISO 27001 certificate. Procurement teams sometimes accept either, which is worth asking before you commit.
How they differ in practice
- Output: ISO 27001 gives you a certificate you can show publicly. SOC 2 gives you a confidential report you share with customers, usually under NDA.
- Scope: ISO 27001 certifies a management system and requires a risk assessment and a Statement of Applicability. SOC 2 starts from the Trust Services Criteria, with Security always in scope and Availability, Confidentiality, Processing Integrity and Privacy added when your commitments call for them.
- Who audits: an accredited certification body for ISO 27001, a licensed CPA firm for SOC 2.
- Timeline: a SOC 2 Type II is gated by its observation window. ISO 27001 requires the management system to have operated, including an internal audit and management review, before the Stage 2 audit.
How much they overlap
Access control, change management, logging, vendor management, incident response, security awareness and risk assessment appear in both. That is why a company that has done one usually finds the second much faster. We plan the controls once and map the evidence to both frameworks.
Which should you do first?
Choose by the customer who is waiting. A stalled US deal points to SOC 2, and a UK or European tender that names ISO 27001 points to that. If neither is urgent, ISO 27001 is often the better long-term foundation because it builds a management system, while SOC 2 can then be added with limited extra effort. Many companies also use a SOC 2 Type I to unblock a deal while the Type II observation window runs.
What it costs
For both, cost has three parts: consultancy support, any compliance tooling you choose, and the auditor's fees, either the certification body or the CPA firm. It depends on your size and scope, so a short scoping call gives a more useful number than a generic range.
Next step
Tell us which customers are asking and in which regions, and we will recommend an order and a realistic timeline. See our SOC 2 page and ISO 27001 page, or book a free advisory session. For US SaaS teams, SOC 2 Type I versus Type II explains the two report types.